OCI coverage
Analyze OCI spend, investigate anomalies, and act on optimization opportunities with approved automated remediation in PointFive OS.
Investigate OCI usage
- Understand spend across your OCI environment
- The same cost analysis you already run on your other clouds, now reading OCI.
- Catch unexpected spend
- OCI is included in PointFive's daily anomaly detection, so unexpected changes in spend surface automatically alongside anomalies from your other cloud providers.
- Optimize and remediate
- Review OCI optimization recommendations and execute approved remediation through PointFive OS. Discovery uses read-only access. Automated remediation uses customer-authorized permissions, and each customer chooses how changes are approved: per change, once for a trusted playbook, or not at all.
OCI coverage details
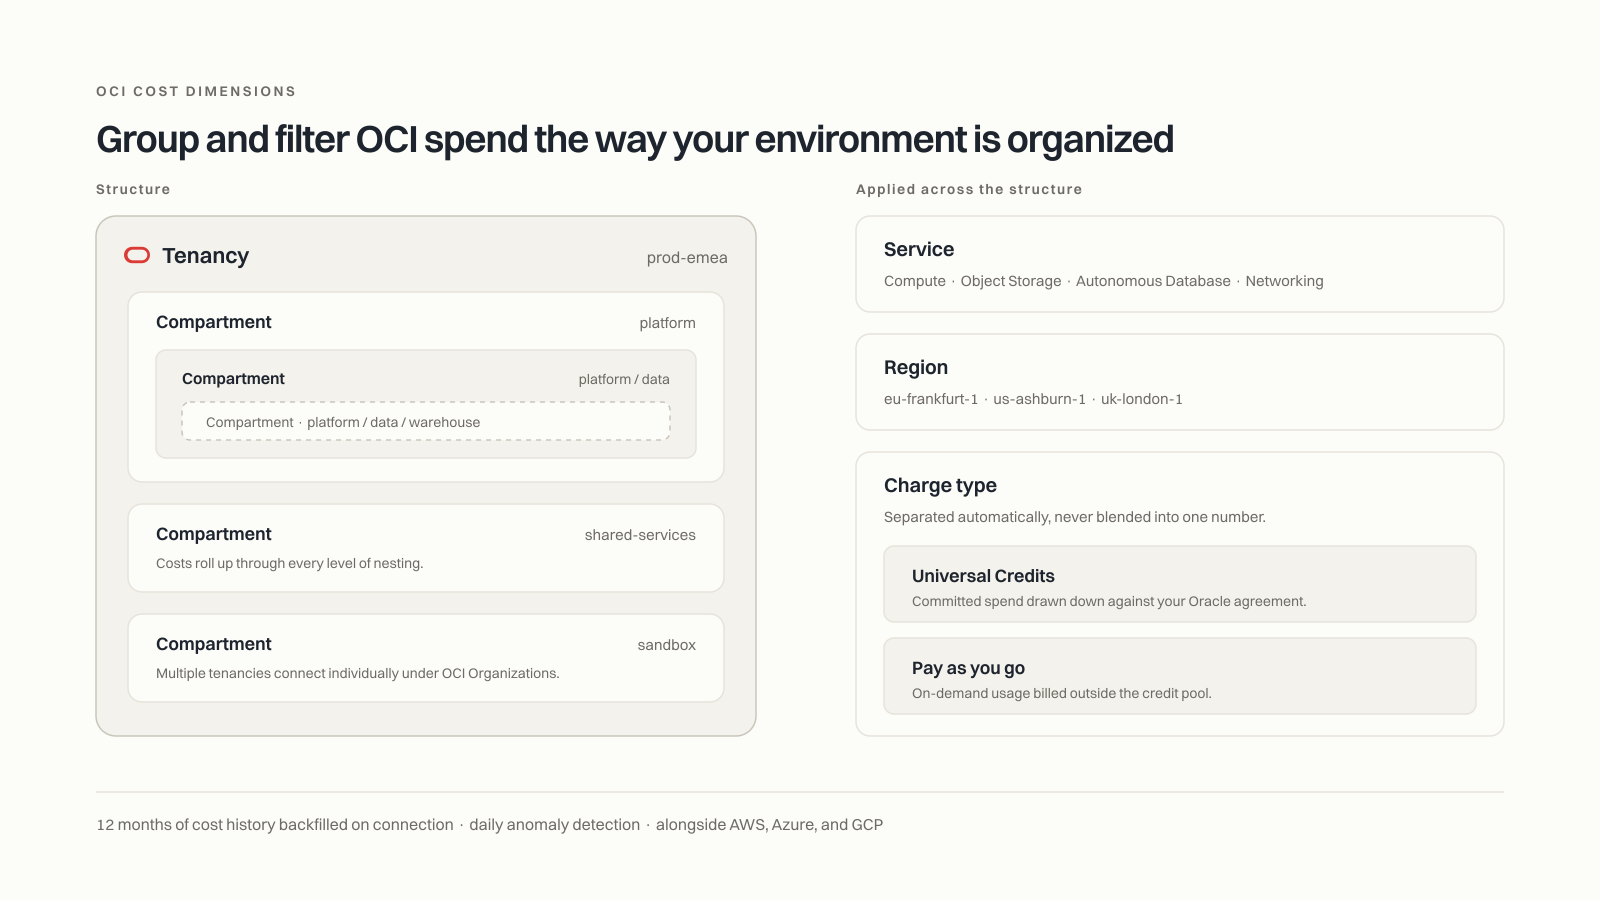
PointFive supports OCI-native dimensions, so you can group and filter spend based on how your tenancies and resources are structured.
| Service or resource | What PointFive analyzes |
|---|---|
| Tenancy | Analyze costs by tenancy, including environments using OCI Organizations with multiple tenancies. |
| Compartment | Attribute costs across OCI compartments, including nested structures. |
| Service | Understand which OCI services are driving spend. |
| Region | Compare costs across OCI regions. |
| Charge type | Separate Universal Credits from pay-as-you-go spend. |
Service or resourceTenancy
What PointFive analyzesAnalyze costs by tenancy, including environments using OCI Organizations with multiple tenancies.Service or resourceCompartment
What PointFive analyzesAttribute costs across OCI compartments, including nested structures.Service or resourceService
What PointFive analyzesUnderstand which OCI services are driving spend.Service or resourceRegion
What PointFive analyzesCompare costs across OCI regions.Service or resourceCharge type
What PointFive analyzesSeparate Universal Credits from pay-as-you-go spend.
One multi-cloud cost view
PointFive gives multi-cloud teams one place to understand spend across AWS, Azure, GCP, OCI, and data platforms such as Snowflake and Databricks. With OCI in that view, teams running Oracle Cloud alongside other providers can analyze costs and investigate anomalies without switching between separate provider dashboards or reconciling spend by hand.
Enterprise-grade security and controls.
Independent audits, clear privacy commitments, and controls that keep your organization in charge. Explore our certifications, security reports, and access safeguards.
Visit our Trust CenterFrequently asked questions
For discovery, PointFive connects through a read-only service user and a PointFive-generated key pair. Deploy the access stack through Terraform, OCI Resource Manager, or Cloud Shell, then provide the service user OCID to PointFive. The private key remains in PointFive. Discovery uses read-only access. Automated remediation uses customer-authorized permissions, and each customer chooses how changes are approved: per change, once for a trusted playbook, or not at all.
PointFive ingests OCI cost data through Oracle's FOCUS report and lets you analyze spend by tenancy, compartment, service, region, and charge type, including Universal Credits and pay-as-you-go spend.
Yes. OCI is available alongside AWS, Azure, and GCP in PointFive, giving multi-cloud teams one place to analyze costs and investigate anomalies across providers.
Yes, from day one. Each tenancy connects individually, the pattern already used for connecting multiple AWS accounts.
A full 12 months of cost history backfills automatically the moment you connect a tenancy.
Yes. PointFive OS supports OCI cost visibility, anomaly detection, optimization recommendations, and approved automated remediation. Discovery uses read-only access. Automated remediation uses customer-authorized permissions, and each customer chooses how changes are approved: per change, once for a trusted playbook, or not at all.
Discovery uses read-only access. Automated remediation uses customer-authorized permissions, and each customer chooses how changes are approved: per change, once for a trusted playbook, or not at all. Key-pair authentication with a PointFive-generated private key. Private key remains in PointFive. Discovery access granted at the tenancy root compartment. No compute, agents, or persistent footprint in your tenancy. Billing data read through Oracle's FOCUS report. Data encrypted at rest. SOC 2 Type II.